mrdtech

Michael Dziegiel

Senior Network & Systems Administrator | Cloud, Security & Automation

Senior Network & Systems Administrator with 20+ years of experience managing, securing, and maintaining enterprise infrastructure. Skilled in hybrid AD/Entra ID, Intune/Autopilot, Meraki/UniFi/pfSense, virtualization, and cloud security. Known for automation, troubleshooting, and securing critical systems.
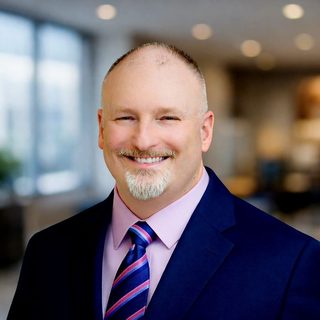
Michael Dziegiel

Projects

Enterprise achievements and homelab builds.

Enterprise & Automation

AD & M365 Onboarding Automation

WPF-based PowerShell GUI automating AD and Microsoft 365 user onboarding — account creation, license assignment, and manager mapping.

SCCM to Intune & Autopilot Migration

Enterprise migration from SCCM to Intune with Autopilot provisioning, Entra ID modernization, and zero-touch deployment.

ConnectWise RMM & Helpdesk Buildout

End-to-end RMM and helpdesk implementation — PSA, patch management, endpoint management, Auvik network monitoring, ScreenConnect, and BrightGauge dashboards.

Enterprise Infrastructure Management

Managing and securing enterprise hybrid infrastructure end to end, spanning network operations, firewalls, VPNs, virtualization, Microsoft 365, Entra ID, Exchange Online, Intune, and cloud identity services.

Homelab & Infrastructure

NOC Dashboard

Self-hosted Network Operations Center dashboard with real-time visibility into Proxmox VMs, Docker containers, UPS status, backup coverage, security posture, and certificate expiry. Multi-user auth, TOTP 2FA, FastAPI + React.

SIEM + CrowdSec Detection

Wazuh SIEM custom detection rules and CrowdSec bouncer configs across a multi-host homelab, with OpenCanary honeypot integration.

Wazuh CrowdSec Security

Prometheus + Grafana Alerting (n8n)

Self-hosted homelab observability — Prometheus + Grafana + node_exporter + cAdvisor across multiple Docker hosts, with alerting via n8n polling the Prometheus API into Telegram (no Alertmanager required).

Prometheus Grafana n8n

UniFi VLAN Segmentation & Firewalls

Zone-based rules, IoT isolation, DNS control, and hardened routing.

AI, Automation & Integrations

Self-Hosted Agentic AI Platform (Hermes Agent)

Architecture and build documentation for a self-hosted Hermes Agent on a dedicated VM: Telegram gateway, read-only MCP gateway, RAG over an Obsidian vault with secrets redaction, and a skill catalog graded by install-source evidence.

Agentic AI Hermes Agent MCP RAG

Vault RAG Pipeline

Self-hosted RAG pipeline for an AI homelab agent — semantic search over an Obsidian vault with automated secrets/IP redaction before embedding, Qdrant + Ollama (nomic-embed-text) + gitleaks.

Qdrant Ollama RAG Python

Multi-Server MCP Gateway

Hardened, read-only MCP gateway exposing Portainer, GitHub, Filesystem, Proxmox, PBS, and Vault RAG visibility to an AI agent — loopback-only, SSH-tunneled, zero client-side credentials.

MCP Docker Security Python

n8n Self-Healing Infrastructure

Automated VM/container recovery, backup-failure alerting, and SIEM event routing to Telegram.

n8n Proxmox CrowdSec

Experience

Systems Administrator — Jeanne D'Arc Credit Union

July 2026 – Present

  • Manage a hybrid Microsoft environment spanning Microsoft 365, Entra ID, and on-premises infrastructure.
  • Administer and troubleshoot Entra ID Conditional Access, secure authentication requirements, policy exclusions, and app access.
  • Lead the enterprise OneDrive for Business rollout, including GPO configuration, pilot testing, troubleshooting, and staged departmental deployment.
  • Implement Microsoft Teams guest and external access security with Conditional Access and MFA controls.
  • Configure Entra ID Company Branding across Microsoft 365 sign-in experiences.
  • Led the migration from legacy Microsoft LAPS to Windows LAPS, modernizing local administrator password management through Active Directory and Group Policy while enforcing stronger 16-character password requirements across enterprise endpoints.
  • Automate administrative tasks and reporting with PowerShell.
  • Support VMware and enterprise networking infrastructure, including VPNs, firewalls, switches, and wireless systems.

Senior Network Administrator — Hans Kissle

Feb 2025 – Apr 2026 · Haverhill, MA

  • Own hybrid infrastructure spanning pfSense firewalls, UniFi switching/wireless, Hyper-V, Ubuntu Server, and Microsoft 365.
  • Administer Azure, Entra ID, Conditional Access, MFA, and AD Connect in a hybrid identity environment.
  • Lead Microsoft 365 services, including Exchange Online, SharePoint, Teams, and licensing automation.
  • Manage Intune MDM/MAM, Apple Business Manager integration, and Autopilot for Windows 365 Cloud PCs and mobile endpoints.
  • Lead the SCCM/MECM to Intune migration with zero-touch Autopilot and Entra ID device modernization.
  • Deploy and maintain Hyper-V and Ubuntu Server workloads with Veeam backup and disaster recovery.
  • Build and maintain helpdesk tooling with ConnectWise RMM/PSA, ScreenConnect, Auvik, and BrightGauge.
  • Automate provisioning, licensing, and compliance reporting with PowerShell, Power Automate, and Microsoft Graph.

Systems Analyst — Skyterra

Sep 2021 – Feb 2025 · Nashua, NH

  • Provide Tier 2/3 support across Azure, Entra ID, Intune, Exchange Online, Teams, SharePoint, OneDrive, and MFA.
  • Administer Active Directory and Group Policy, including OUs, security configurations, and GPOs.
  • Manage Intune endpoint administration, device provisioning, security policies, and application packaging/deployment.
  • Design and implement Intune configuration profiles to enforce application blocking, browser restrictions, and long-path support.
  • Monitored servers and backup systems, performed file restorations, and investigated and resolved network and system issues.
  • Automate routine administrative tasks with PowerShell.
  • Support Conditional Access, PIN-based access, and Microsoft LAPS credential management.
  • Administer Mimecast and Cisco Umbrella for email and DNS-layer threat protection.

Network Technician — GID

Apr 2011 – Aug 2021 · Boston, MA

  • Support Cisco/Meraki infrastructure for VPN, Wi-Fi, VoIP, switching, and security appliance deployments.
  • Administer Active Directory for users, groups, workstations, permissions, and policy support.
  • Build Windows images and locked-down kiosk GPO configurations for controlled-use endpoints.
  • Provide Tier 2/3 support, remote site installations, and escalation support for complex infrastructure issues.
  • Monitor Meraki networks for outages and performance issues.
  • Coordinate tablet/mobile device rollouts, OneDrive adoption, Teams support, and VeraCrypt full-disk encryption.
  • Deployed and configured Meraki MX/MR infrastructure for site-to-site VPN connectivity and Cisco ISR routers with IP phones for VoIP across multiple sites.
  • Support infrastructure deployments and hardware lifecycle tracking across multiple properties.

Skills & Stack

Platforms

Windows Server, Azure, Entra ID, Intune, Autopilot, Active Directory / Group Policy, Microsoft 365, Exchange Online, SharePoint, OneDrive for Business, Microsoft Teams, Windows 365 Cloud PCs, VMware vSphere, Hyper-V, Proxmox, pfSense, UniFi, Meraki, Linux, Apple Business Manager

Networking & Security

Routing, Switching, VPN, VLANs, DNS / DHCP, MFA, Conditional Access, Intune Compliance & Configuration Policies, LAPS, BitLocker, IDS / IPS, Firewall / WAF Management, Network Segmentation, Wireless, Zero Trust (Cloudflare Access / Tunnel), DNS Filtering, DMARC, FortiGate Firewalls, Aruba Switching & Wireless, Cisco Umbrella, Wazuh, CrowdSec

Tools & Tech

Sophos, Proofpoint, ConnectWise RMM, ConnectWise Manage, Auvik, ScreenConnect, CrowdStrike, Arctic Wolf, Mimecast, Veeam Backup & Replication, Veeam Backup for Microsoft 365, ManageEngine, PowerShell, Power Automate, Microsoft Graph API, Git, GitHub, Docker, Portainer, KnowBe4

Automation & Monitoring

AI Agents, MCP, RAG, n8n, Telegram Alerting, Grafana, Prometheus, Automated Alerting, Self-Healing Workflows

Get in touch

Best reached via email.